From Building Websites to Finding Bugs: My Journey Into Cybersecurity
I'm Aathil Ducky. Here's how I started learning web development in 2020, discovered ethical hacking, and became a security engineer while continuing to build and create.
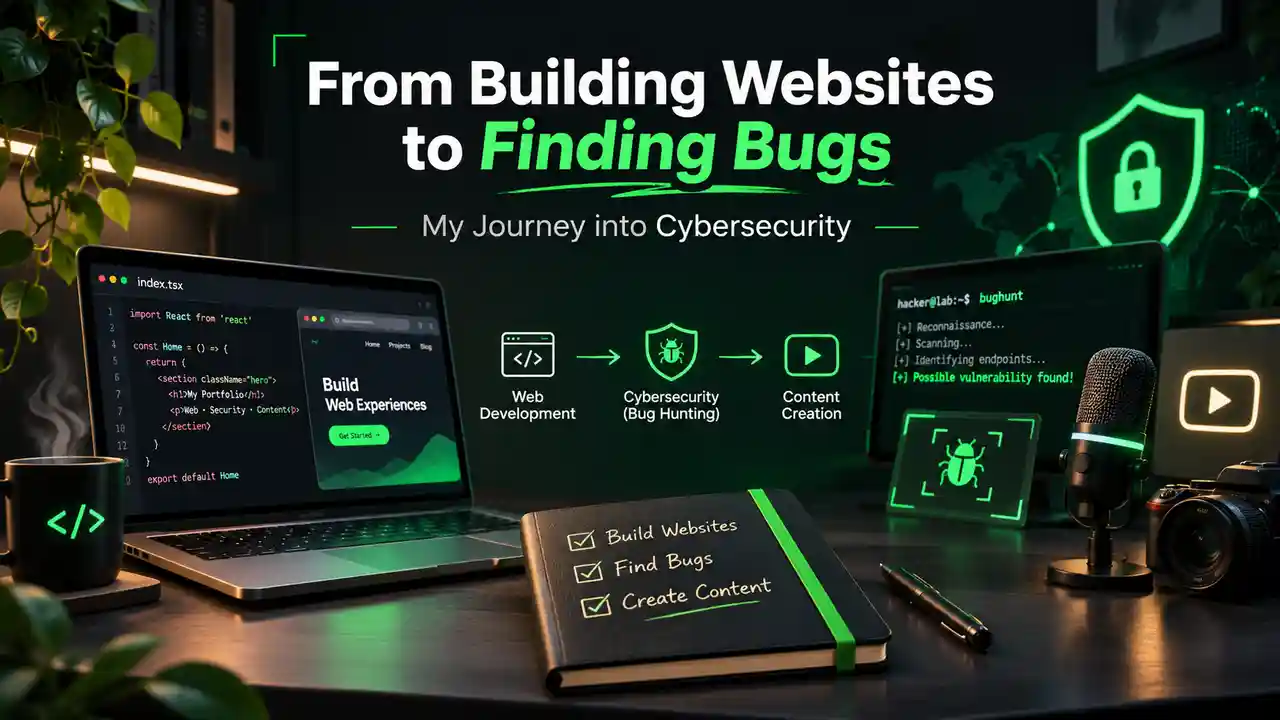
From Building Websites to Finding Bugs: My Journey Into Cybersecurity
Hi, I'm Aathil Ahamed, and online I go by Aathil Ducky.
I started with web development, became curious about how websites could be hacked, and eventually found my way into cybersecurity. This is the story of how it happened.
It started with web development
My tech journey began in 2020, after I finished my A-levels.
I started learning HTML, CSS, and JavaScript because I wanted to build websites. At first, I was just trying to understand how things worked. Then I moved on to MySQL and started creating my own websites and experimenting with web applications.
The more I built, the more I wanted to learn. I liked taking an idea, writing code, and seeing it work in a browser. I also enjoyed finding different ways to solve problems through programming.
How I discovered ethical hacking
Later, I came across something new to me: hacking and bug bounty hunting.
I started reading about HackerOne and the people finding security vulnerabilities through bug bounty programs. I spent time reading articles and write-ups from bug bounty hunters, trying to understand how they found bugs in web applications.
That got me interested in a different side of technology. Until then, I had mostly focused on building websites. Now I wanted to understand how they could have security weaknesses too.
That curiosity led me into cybersecurity and ethical hacking.
Learning by practicing
I learned a lot from online resources, but I didn't want to stop at reading or watching tutorials. I wanted to try things myself.
Some of the platforms I used were:
- TryHackMe — to learn cybersecurity concepts and practice in guided labs.
- Hack The Box — to work through hacking challenges and vulnerable machines.
- PortSwigger Web Security Academy — to learn about web application vulnerabilities through hands-on labs.
- VulnHub — to download vulnerable machines and practice in my local lab.
I also set up vulnerable applications and machines locally so I could practice in my own environment.
I kept exploring web applications, testing what I'd learned, and reading more whenever I came across something I didn't understand. Along the way, I also wrote articles about what I was learning and continued building web applications.
Building applications and finding bugs became two things I genuinely enjoyed.
From learning to real work
I spent two years working as a web developer, building websites and improving my programming skills. I also took on freelance work, which I continue to do.
At the same time, my interest in security kept growing. That eventually led me to Welford Systems, where I now work as a Security Engineer.
My work includes testing Identity and Access Management (IAM) and Identity and Access Governance (IAG) systems. So far, I've identified and reported more than 100 vulnerabilities in the systems I've worked on. I also tracked those issues and followed their progress as they were fixed.
For me, this work connects both sides of my journey: understanding how applications are built and investigating where security problems can appear.
Why I'm starting this blog
Even while working in cybersecurity, I haven't stopped enjoying programming, researching new things, or building solutions to problems.
Recently, I've also become interested in content creation. I want to share more of what I learn and explore, instead of keeping it all to myself.
That's why I'm building my personal website and writing this first blog post.
This space is where I want to share my experiences with web development, cybersecurity, ethical hacking, and the things I build and learn along the way.
I started in 2020 by learning how to create a simple website. I didn't expect that interest to lead me into finding security vulnerabilities and working as a security engineer.
I'm still learning, still building, and still exploring.
Thanks for being here.
— Aathil Ducky
aathilducky.com